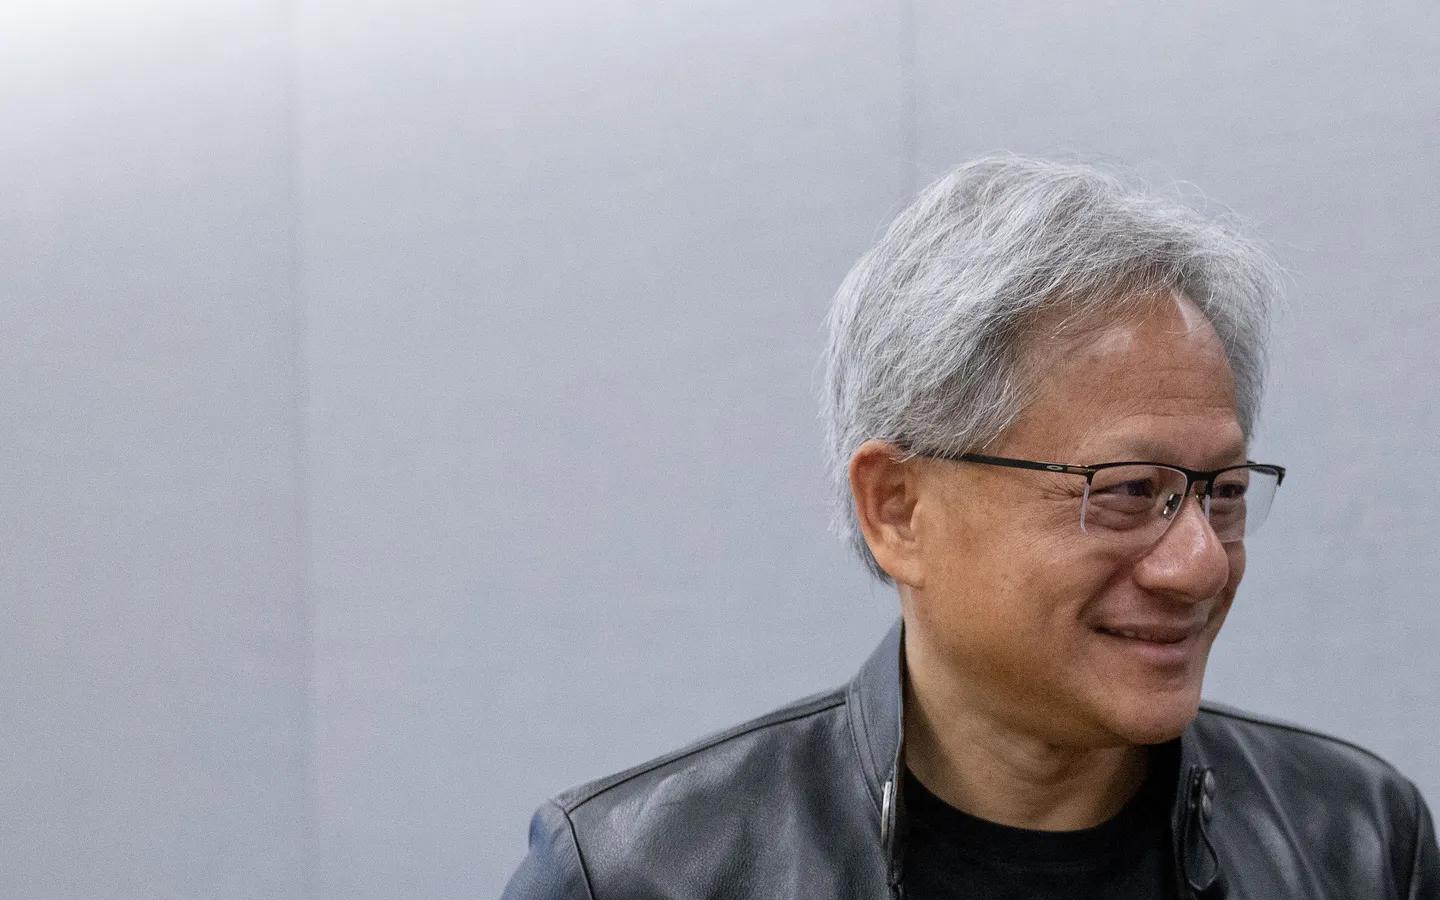
Nvidia's board is investigating its own chief executive. On 8 November 2026 the board said that “a committee of independent directors, assisted by outside independent counsel, will oversee the investigation”, after reports that Jensen Huang had been targeted by Chinese intelligence through a relationship with a woman who was an executive at a Singapore company that bought Nvidia's chips. The same day, Huang admitted in a memo to staff that he had been unfaithful to his wife, without naming the person.
The board says it “has no reason to believe that either national security or Nvidia secrets were compromised”, and China has dismissed the reports. According to the company, the committee has since hired Joon H. Kim of Wachtell, Lipton, Rosen & Katz, a former acting US Attorney for the Southern District of New York. Nothing about espionage has been found or proven.
Whatever the inquiry finds, the board did two things right. A committee with no reporting line to the CEO took control, and it hired its own outside counsel. Both follow the one principle every corporate governance framework rests on: nobody oversees themselves.
The rules cited here are US and UK. This is general guidance, not legal advice for a specific case.
What is a corporate governance framework?
A corporate governance framework is how a company makes sure the right checks and balances are in place, from the policies and the board down to the procedures, channels, approvals and workflows that run it day to day, and it breaks down into the five layers below.
| Layer | The question it answers | What sits in it |
|---|---|---|
| Board | Who is in charge, and who checks the CEO? | Independence, committees, chair and CEO roles |
| Decision rights | Who can decide what? | Reserved matters, delegation of authority |
| Risk and control | How does the board know what could go wrong? | Risk register, internal controls, internal audit, reporting lines |
| Conduct | How are people kept honest? | Code, conflicts, gifts, third parties, speak-up, investigations |
| Accountability | How does the company answer for itself? | Pay and clawback, succession, disclosure |
Where the rules for each layer come from depends on where a company is listed. The US has no single governance code. It relies on state company law, mostly Delaware's, together with SEC rules and the NYSE and Nasdaq listing standards.
The UK has one code, the UK Corporate Governance Code, which listed companies apply on a comply-or-explain basis: they follow each provision or say publicly why they do not. The G20/OECD Principles of Corporate Governance are the global reference that many national codes draw on.
Board governance: who checks the CEO
Governance starts with shareholders, who elect the board, and the board appoints and oversees the CEO, who runs the company through management. The board approves the strategy and budget, checks results against them and decides who leads the company.
The board can only check the CEO if enough of its members are independent, meaning they do not work in the business and have no ties that would compromise their judgment. NYSE and Nasdaq rules require a majority of independent directors at most listed companies, and the UK Code expects at least half the board, excluding the chair, to be independent. Independent directors should meet without management regularly, and at least twice a year.
The most basic check on a chief executive is a separate chair. The UK Code says one person should not hold both roles. Many US companies combine them and appoint a lead independent director instead, who chairs sessions without the CEO and is the route for concerns about the CEO. The UK has a similar role, the senior independent director.
For a company in Nvidia's position, this lets independent directors act without the chief executive, because they can convene on their own and the lead independent director is their route for concerns about the CEO.
Most boards work through three committees. The audit committee oversees financial reporting, internal controls and internal audit, the nominating committee handles board appointments and succession, and the compensation committee, called the remuneration committee in the UK, sets executive pay. Banks and some other companies add a risk committee, and elsewhere the audit committee usually owns risk.
The board also sets the culture. The UK Code asks boards to assess and monitor culture, and a framework fails in practice if directors make exceptions for the CEO. In Delaware, the Caremark decision of 1996 expects directors to make a good-faith effort to put a reporting system in place for the risks that matter most.
Decision rights and delegation of authority
The board cannot make every decision, so it needs a written record of which decisions it keeps and which it hands down. Most boards keep a schedule of reserved matters, covering items such as strategy, major acquisitions, large capital spending, dividends and senior appointments.
Below that sits a delegation of authority, which sets out who in management can approve what, and up to what value. Clear limits stop one person from committing the company alone, and they show auditors and investigators whether a decision was properly made.
The rule that matters most is that nobody approves their own business. The CEO's expenses, travel and outside roles should be approved by the chair or a committee, and transactions between the company and its directors or executives should be reviewed by the audit committee or another independent body, as NYSE and Nasdaq rules expect.
A company in Nvidia's position should apply the same rule to relationships. When an executive has a personal relationship with someone at a customer, decisions about that customer's pricing, supply and credit should move to someone else, and the executive should step aside.
Risk register and internal controls
A risk register is a running list of the risks the company knows about. It records who owns every risk, how likely and serious it is, the controls in place and the actions still open. The UK Code asks boards to assess the company's emerging and principal risks, and a register is how most companies do it.
Review the register at least quarterly, and include people risks as well as financial ones. That means dependence on one leader and insider threats, which the US Cybersecurity and Infrastructure Security Agency says can include espionage.
For a company in Nvidia's position, foreign intelligence targeting of senior executives belongs on the register as its own entry, owned by someone such as the chief security officer. Its controls should include briefings before high-risk travel, a way to report a suspicious approach without it being treated as an admission, and relationship declarations, reviewed by the committee every quarter.
Internal controls are the checks that make sure transactions are approved, recorded and reported correctly. In the US, section 302 of the Sarbanes-Oxley Act requires the CEO and CFO to certify each periodic report, and section 404 requires management to assess internal control over financial reporting every year. In the UK, the Code asks boards to declare whether their material internal controls are effective, for financial years starting on or after 1 January 2026.
Internal audit tests those controls, so its main reporting line is to the audit committee, with the CEO as its administrative line. The committee approves the head of internal audit's appointment and removal, as the Institute of Internal Auditors' Global Internal Audit Standards require.
The heads of compliance and investigations usually report day to day to the CEO or general counsel, with a direct line to the audit committee, and the committee should also approve their appointment and removal. The Justice Department's Evaluation of Corporate Compliance Programs asks whether compliance can reach the board directly, and the answer affects how a company is charged.
Conduct
Conduct starts with a code of conduct that staff confirm each year they have read. The processes below keep relationships, gifts and third parties in view, and then catch and handle problems when they happen.
Conflicts of interest and gifts
A conflict of interest arises when someone's personal interests could sway their decisions at work, such as a stake in a supplier or a close relationship with someone at a customer. Ask directors and senior staff to declare interests once a year and anything new within 30 days, and have someone independent review each declaration. For directors and the CEO, that means a board committee.
US-listed companies must disclose related person transactions over $120,000 under Item 404 of Regulation S-K. Item 404's definition stops at immediate family and people sharing a household, so a relationship outside the home is not caught, and your policy should ask about those relationships directly. The conflict of interest policy template and declaration form are a starting point.
In a company in Nvidia's position, a declaration that asks about close personal relationships at customers would put a relationship like the one in the reports in front of a board committee, which should record its decision and any safeguards.
A gifts and entertainment register records the gifts, meals and events staff give or receive, with a value above which they must record a gift and a higher value above which they need approval. Under section 7 of the UK Bribery Act 2010, a company is guilty of failing to prevent bribery unless it had adequate procedures, and a register is part of the evidence. Hospitality from a customer's executives should go on the register as well.
Third parties
Check who owns and runs your customers and suppliers, not only whether they pay. Export control guidance already expects this of chipmakers. The Commerce Department's guidance on chip diversion tells exporters to check a customer's incorporation date, ownership and end user, and because the woman in the reports was an executive at a customer, a company in Nvidia's position should extend those checks to a customer's owners and key people. The due diligence questionnaire covers the questions to ask.
Speak-up
Tips are the most common way fraud is found. The ACFE's 2024 Report to the Nations found they uncovered 43% of cases, more than three times any other method. In the US, section 10A(m)(4) of the Securities Exchange Act makes the audit committee responsible for a confidential, anonymous channel for accounting concerns, and Provision 6 of the UK Code sets a similar expectation for the whole workforce.
The routing rule matters more than the channel. Reports that name an executive, a director or the heads of legal, compliance, investigations or internal audit should go straight to the audit committee chair, and the person named should never be able to see them. When a report could involve the general counsel, I would make the chair the only recipient. At a company in Nvidia's position, an employee with a concern about the chief executive should have a route that ends with the audit committee chair, not with management.
I saw what happens without that rule at Wirecard. In the middle of my own investigation the company set up a whistleblowing channel, and when I asked where it went, I was told it went to Jan Marsalek, the executive who later fled and is still wanted.
Who investigates the CEO: the special committee
Every structure has a gap at the top of its own chain, so write down in advance who handles each case. The UK's Association of Corporate Investigators requires investigators to be free from conflicts of interest and undue influence, and this table applies that to each level of seniority.
| Subject of the report | Who receives it | Who decides scope | Who investigates |
|---|---|---|---|
| Employee or manager | Investigations team | Head of investigations | Internal investigator |
| Executive committee member | Audit committee chair and compliance officer | Audit committee | Independent internal team or outside counsel, reporting to the committee |
| General counsel or compliance officer | Audit committee chair | Audit committee | Outside counsel; the subject is recused |
| Head of investigations or internal audit | Audit committee chair | Audit committee | Another function or an outside firm |
| CEO or board chair | Audit committee chair or lead independent director | Special committee of independent directors | Outside counsel retained by the committee |
| Audit committee member | Board chair or lead independent director | The board, without that member | Outside counsel |
When the CEO is the subject, the board usually forms a special committee, as Nvidia's did. Its members should have no business, family or social ties to the CEO, and it should hire its own lawyers. The workplace investigation guide covers the steps of an investigation in detail.
Accountability
The compensation committee should link pay to long-term results and be able to recover it when things go wrong. Under the SEC's Rule 10D-1, US-listed companies must have a policy to recover incentive pay awarded in error after an accounting restatement. The rule is triggered by a restatement, not by misconduct, so many boards add a wider clawback for serious misconduct, and the UK Code expects schemes to let the company withhold or recover awards.
Succession is the board's answer to key person risk. Nvidia's shares fell 4.3% on the first trading day after the investigation was announced, wiping nearly $200 billion off its value. The nominating committee should keep an emergency plan that names an interim leader, sets out who speaks for the company and lists the decisions that need board approval while an investigation runs.
A governance crisis quickly becomes a disclosure question. US-listed companies must file a Form 8-K within four business days if their principal executive officer retires, resigns or is terminated, and UK-listed companies must disclose inside information as soon as possible under the Market Abuse Regulation. No rule specifically requires announcing an internal investigation, so the board has to judge whether it is material. Nvidia's statement came from the board, not management, which is the right owner when the CEO is the subject.
Test the route before you need it
Pick the most senior person in your company and imagine a report about them arrives tonight. Write down who would receive it, who would choose the investigator and who could see the file. If any answer leads back to that person or their team, fix it first, then repeat the test once a year with a real test report and give the result to the audit committee.
Confide runs the conduct layer of this framework, from conflict declarations, gifts registers and third-party checks to speak-up and investigations. Each type of case can follow its own SOP, which can trigger any event in the workflow, including approval steps and a legal hold. If a user is named in a report, Confide automatically revokes their access to that case, and an audit trail that cannot be changed records every access and action.
To see the route working, book a demo of Confide's whistleblowing software and watch a report about an executive go to the audit committee chair while the executive is locked out of the case.
Corporate governance framework FAQ
Why is corporate governance important?
It decides whether problems reach people who can act on them before they turn into crises. Good governance keeps a company within the law and gives shareholders, lenders and regulators a reason to trust its numbers, and when it fails the cost can include fines, lawsuits against directors and lost market value.
What is an example of corporate governance?
Nvidia's response to reports about its chief executive in November 2026 is a current example. The board formed a committee of independent directors to oversee the investigation, and that committee hired its own outside counsel instead of leaving the inquiry with people who report to the CEO.
What is the difference between corporate governance and compliance?
Corporate governance is how the whole company is directed and checked, from the board down. Compliance is one part of it: making sure the company follows the law, its regulators' rules and its own policies, and reporting to the board on how well that works.
Does a private company need a corporate governance framework?
Yes, though fewer rules apply. In the UK, very large private companies must report on their governance arrangements, and many use the Wates Principles to do so. In the US no code applies to private companies, but investors, lenders and acquirers still expect independent oversight, clear decision rights and a way to raise concerns.
How often should a board review its governance framework?
At least once a year, usually led by the company secretary or general counsel. The review should cover each committee's terms of reference, the reserved matters and delegation of authority, and whether the board's own evaluation found gaps.